Code & application review
A read of your codebase for security flaws, fragile patterns, and risky shortcuts.
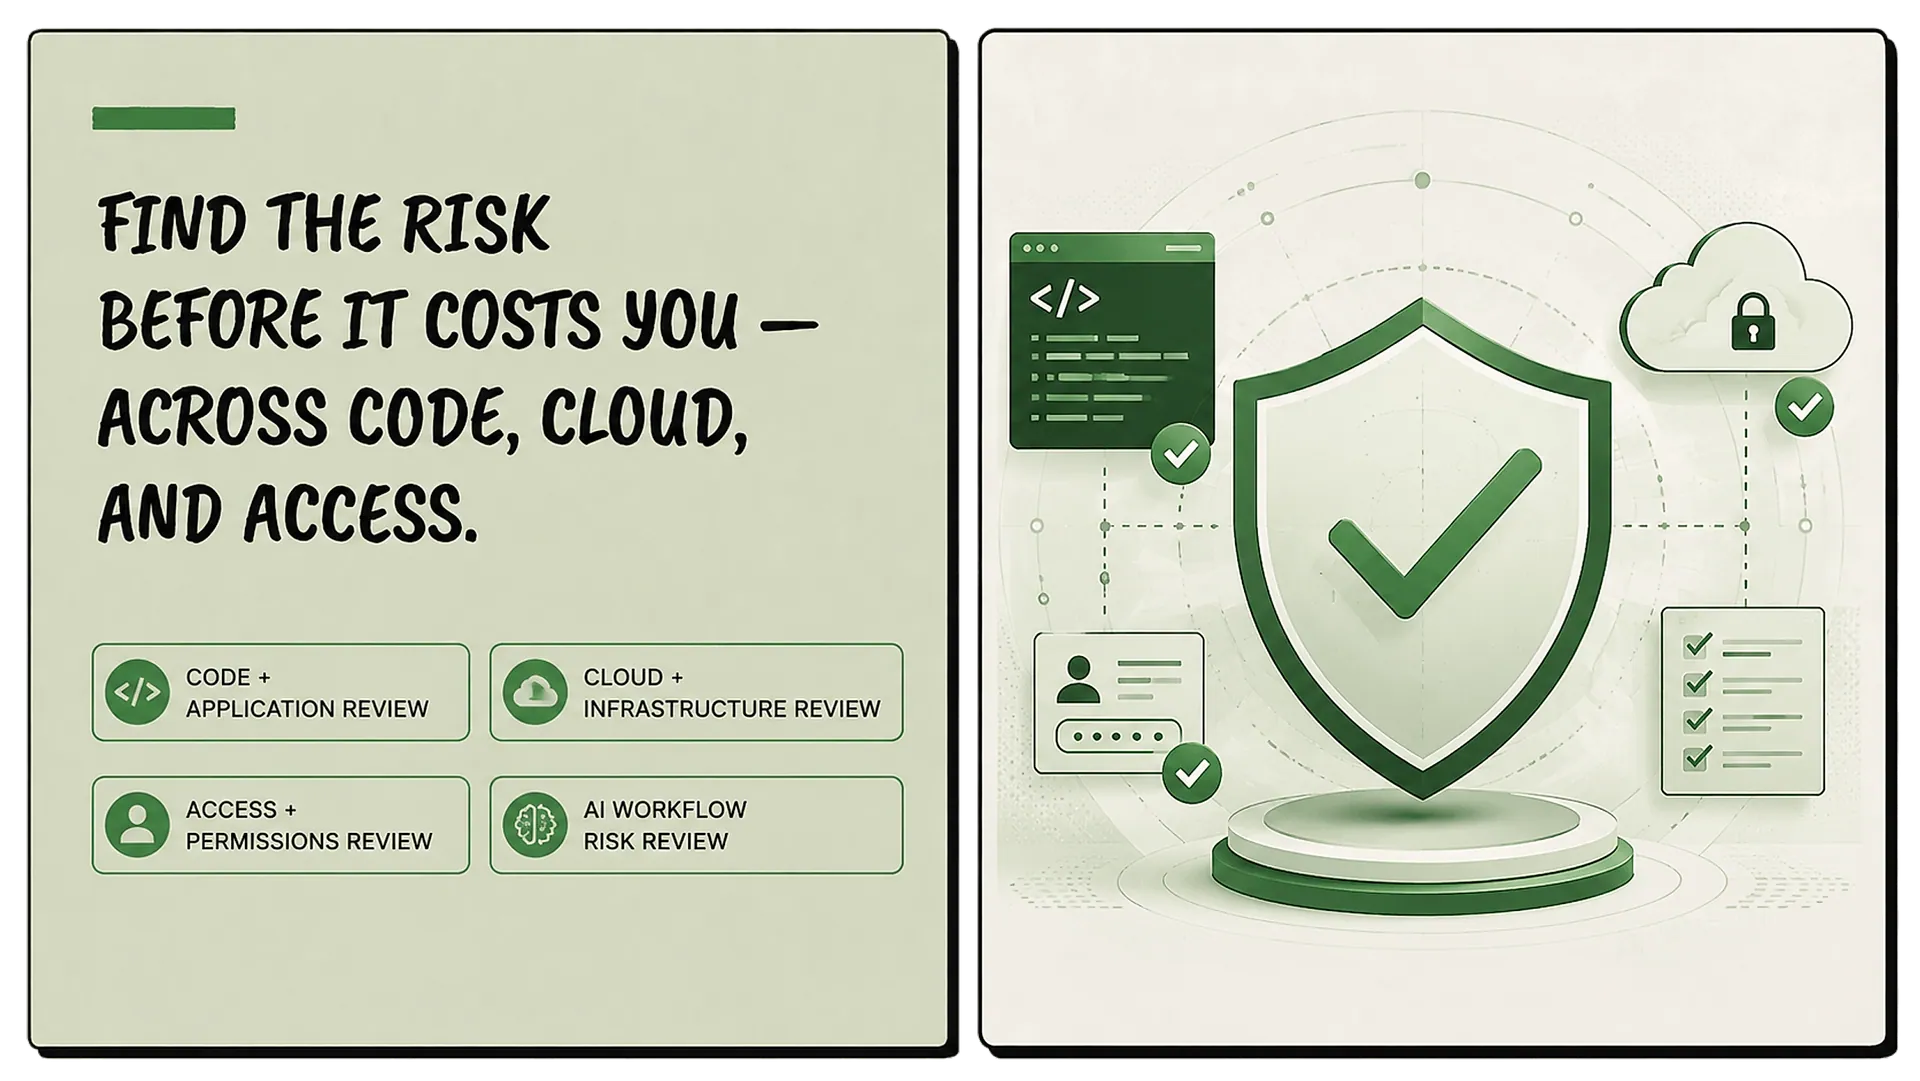
We review your code, cloud setup, access controls, AI workflows, and deployment process.
You're about to ship software, but nobody has checked it for security holes.
You've inherited a system and don't know what risks are hiding inside it.
Access, credentials, and permissions have grown messy as the team scaled.
You're adding AI to your product and aren't sure where it can be trusted.
A read of your codebase for security flaws, fragile patterns, and risky shortcuts.
A review of your cloud setup for misconfigurations and weak defaults.
Who can reach what, and where permissions should be tightened to least privilege.
Where AI can fail, and where a human needs to stay in the loop.
We agree what's in scope - code, cloud, access, AI, deployment.
We work through the systems methodically, documenting risks with evidence.
We rank every finding by severity and likelihood.
Once you've addressed the priorities, we re-check the important ones.
The people who scope your project build it.
Nothing ships until an engineer has signed off on it.
Access controls and audit trails that hold up to scrutiny.
The full codebase, documentation, and credentials - no lock-in.
Monthly support to fix, patch, and improve.
What's realistic and what it costs, before you commit.
Whatever's in scope: source code, cloud and infrastructure setup, access and permissions, AI workflows, and the deployment process. We agree the boundaries with you before we start, so you know exactly what's covered.
It's a risk-focused engineering review, not an accredited audit or formal certification. It's designed to find and prioritise real, fixable risks before they cause problems. If you need formal penetration testing or compliance certification, we'll say so and help you scope it.
Yes. Reviewing inherited or third-party software is one of the most common reasons teams come to us. We document what's there, surface the risks, and give you a clear plan to make it safer.
A prioritised report: every finding ranked by severity, with practical steps to fix it, plus a plain-language summary for stakeholders. After you've made the changes, we re-check the high-priority items.
You get a prioritised, plain-language report of the real risks in your code, cloud, and access.